By clicking “Accept”, you agree to the storing of cookies on your device to enhance site navigation, analyze site usage, and assist in our marketing efforts. View our Privacy Policy for more information.
How to Build a Cybersecurity Supply Chain Risk Management Programme
Build an effective C-SCRM programme. Here’s how to tier suppliers, assess controls, monitor risk, respond to incidents and report progress.
Risk Ledger
|
Company
November 20, 2026
|
25
mins read
Share
Quick answer
Cybersecurity supply chain risk management (C-SCRM) is the security-led practice of identifying, assessing and reducing the cyber risk that reaches your organisation through suppliers, their own suppliers and the software you depend on.
Tier suppliers by business impact rather than spend, looking at the services they support, the data and access they hold, and how quickly you could recover or replace them.
Set assessment depth by tier, so critical suppliers get validated evidence, continuous monitoring and incident playbooks while low-risk suppliers get baseline checks and contract clauses.
Use questionnaires and continuous monitoring together. Questionnaires cover internal controls you can't observe from outside, and monitoring shows what changes between formal reviews.
Trigger a reassessment whenever something material changes, such as a supplier breach, an acquisition, a new subcontractor or expanded access to your data.
Map fourth parties for your critical suppliers first, then look for providers several of them share, because one outage there can take out multiple services at once.
Cybersecurity Supply Chain Risk Management (C-SCRM) identifies, assesses and mitigates cyber risks that emerge from today’s interconnected supply chains.
Every large organisation now relies on external suppliers to deliver their critical services. But these direct suppliers also depend on a wide network of suppliers themselves, exposing you to supply chain cyber risks from beyond your direct vendors.
From supplier and software compromises to fourth-party and concentration risks, cyber risks travel through your digital supply chain connections and can disrupt your systems, data and services without directly penetrating your IT perimeter. Security leaders are aware of this, but they’re on the back foot: only 30% can see their entire network of supply chain connections, let alone have the capacity to manually assess each supplier.
That’s why a robust and active C-SCRM programme that helps you prioritise, assess and remediate supply chain cyber risks is no longer a choice; it’s a governance and resilience imperative.
This guide will show security leaders how to build or improve their C-SCRM programme by providing actionable advice on:
Implementing C-SCRM frameworks
Identifying and tiering critical suppliers
Assessing and monitoring supplier cybersecurity risk
Responding to supply chain incidents
Reporting on C-SCRM progress
What is cybersecurity supply chain risk management?
Cybersecurity Supply Chain Risk Management (C-SCRM) focuses on the disruptions that could reach you through digital supply chain connections, such as a malicious software update or a data breach at a SaaS provider. An effective C-SCRM programme helps you manage these cyber risks at every stage of the digital supply chain lifecycle - from assessing your critical supplier relationships to responding to supply chain incidents.
This is crucial for modern organisations. According to the UK’s National Cyber Security Centre (NCSC), “many companies lose sight of their supply chains” beyond third parties, but they don’t lose the risk exposure. 82.4% of organisations suffered at least one supply chain cyber incident in the past 12 months and 65% of large organisations consider supply chain vulnerabilities their number one cyber challenge in 2026 (up from 54% in 2025).
As security leaders ramp up efforts to address these supply chain cyber risks, attention has turned to C-SCRM to boost supplier assurance and enhance operational resilience.
What cybersecurity supply chain risks should organisations prioritise?
Be it a security breach at a direct supplier or a fourth-party concentration risk, the significance of a supply chain cyber risk depends on which of your suppliers are affected, the business services they support and the data access they have. Or, in other words, you should prioritise cyber risks according to their potential disruptive impact on your business.
Here’s a list of the most common cybersecurity supply chain risks.
Supplier data breaches. When your customer, employee or operational data could be exposed if a supplier’s systems are compromised.
Compromise of privileged supplier access. When an attacker breaches a supplier who has privileged access to your data and systems.
Operational disruption at a critical provider. When one of your critical suppliers goes offline due to an outage, breach or ransomware attack, preventing you from accessing its services.
Software or open-source vulnerabilities. When vulnerabilities in software or open-source components flow downstream into your systems. This can be accidental or purposeful (i.e. an attacker inserting malware into a software package).
Weak supplier security controls. If a direct supplier fails to have basic security controls, such as multi-factor authentication (MFA), or does not adhere to key standards like Cyber Essentials, these vulnerabilities become your vulnerabilities.
Fourth-party exposure. When an outage or incident occurs at your supplier’s supplier (fourth-party) that can affect your suppliers or ability to deliver critical services.
Cloud and platform concentration risk. When many of your critical suppliers or services depend on the same SaaS platform or Cloud provider.
Single points of failure. When multiple suppliers depend on the same shared provider, this single point of failure going down can affect how your entire business operates.
Inadequate supplier incident notification. When an affected supplier doesn't tell you about an incident until it’s too late.
Limited substitutability or long recovery times. When you rely on a specialist supplier that’s not easy to replace or takes weeks to recover after an incident.
Geographic, geopolitical or jurisdictional dependencies. When your critical operations sit within the same region and could be derailed by a natural disaster, energy grid failure or political unrest.
Grouped together, these common cyber risks fall into four main categories: direct supplier risks; dependency risks; fourth-party risks and software risks. Each category has a different impact on your business and requires different controls.
How is cybersecurity supply chain risk management different from third-party risk management?
Cybersecurity supply chain risk management (C-SCRM) or third-party risk management (TPRM)? It can quickly get confusing, especially when they’re (wrongly) used interchangeably.
While there are overlapping elements, such as assessing the cybersecurity controls of a direct supplier, the risks and scope of C-SCRM and TPRM are inherently different. Here’s the key differences.
Third-party Risk Management: TPRM covers all risks that emerge from working with external parties, including financial, legal, operational and cybersecurity risks. Due to its broad scope, the responsibility for TPRM usually falls across the procurement, risk and compliance teams. They assess and govern engagement with third-party suppliers and partners, usually through questionnaires at onboarding and periodic assessments. While traditional TPRM assessments provide a snapshot of your direct suppliers’ security postures, they struggle to show changing risks or risks beyond direct vendors.
Cybersecurity supply chain risk management: C-SCRM concentrates on the risks posed by cyber threats and digital dependencies across the supply chain. With its focus on digital supply chain security, emanating from the likes of source code, build systems, and development pipelines, responsibility for C-SCRM falls into the cyber security leader’s camp. C-SCRM assessments and continuous monitoring helps security leaders find, evaluate and manage cyber risks at every stage of the digital supply chain lifecycle, including breaches, outages, software compromises and concentration risks.
Which frameworks and regulations shape cybersecurity supply chain risk management?
In 2008, the US National Institute of Standards and Technology (NIST) played a key part in formalising the concept of cybersecurity supply chain risk management by launching its C-SCRM programme. Through its frameworks and guidance like NIST SP 800-161 and CSF 2.0, it remains the go-to source of what good looks like in C-SCRM, but it’s not the only show in town. Here are the key frameworks, standards and regulations to follow.
NIST SP 800-161
This is NIST’s detailed guidance on C-SCRM, covering strategies, policies, implementation plans and risk assessments. It also provides advice on controls, metrics, risk appetite and supplier inventory. Use the latest version of the text (it was last updated in 2024) to help structure your C-SCRM programme, but make sure to adapt the guidance and frameworks to your organisational context. For example, select the controls that fit your supplier ecosystem and risk tolerance.
NIST Cybersecurity Framework 2.0
Known as CSF 2.0, this NIST framework provides a structure for integrating cybersecurity into enterprise risk management. In particular, it frames cybersecurity risk as a senior leadership responsibility and governance issue rather than a procurement afterthought. It highlights high level cybersecurity outcomes that can be used by any organisation, but does not prescribe how these outcomes should be achieved (instead linking to online resources).
NIST C-SCRM Quick-Start Guide
Leaders building their first C-SCRM programme, this is for you. Instead of trawling through SP 800-161 or CSF 2.0, this Quick-Start Guide provides a more accessible route into applying C-SCRM. For example, the guide includes checklists on the requirements suppliers must follow and helps you establish baseline C-SCRM capabilities. However, while a quick-start is great for organisations with no existing supply chain programme, it’s not comprehensive enough for mature organisations.
NCSC guidance
The UK's NCSC’s guidance defines the essential principles of supply chain security and what you should expect from suppliers. Focused on medium to large organisations in the UK, the NCSC guidance explains how to understand supplier risks, establish control, check your arrangements and improve continuously. For example, it shows how supplier criticality is key to assurance assessments and how to map your supply chain.
ISO 27001
This renowned security standard outlines how to handle supplier risk using controls on supplier relationships, supplier agreements, and the general digital supply chain, as well as guidance on monitoring and change management. Thanks to its control-based approach, it's perfect as evidence in supplier audits, but is less prescriptive than NIST on how deep supplier assessments should go.
Regulations
Those standards and frameworks are optional. These regulations are not. Designed to ensure operational resilience in the face of supply chain cybersecurity threats, the following regulations must be taken into account when building a C-SCRM programme (depending on your industry and location).
NIS2 (EU): The NIS2 Directivehighlights how entities must address their relationships with direct suppliers and service providers, including how to weigh up supplier vulnerabilities and practices.
DORA (EU financial sector): Much of the detail revolves around the implementation of technical standards, but DORA also requires a register of digital arrangements, pre-contract due diligence and concentration risk assessments.
The Cyber Security and Resilience Bill (UK): If made law, the Bill will expand the scope of the NIS regime to capture additional types of third-party suppliers, including Managed Service Providers (MSPs) and data centres, and enable regulators to identify ‘designated critical suppliers’ that they deem a concentration risk.
Financial services (UK): The Bank of England, PRA and FCA oversees rules about C-SCRM, especially third parties. For example, the BoE/PRA’s SS1/21 dedicates a whole chapter to mapping external suppliers that support important business services, while PRA SS2/21 calls on you to periodically assess third parties, manage concentration risks and monitor fourth party dependencies.
C-SCRM frameworks and regulations at a glance
Framework or regulation
What it provides
Best used for
NIST SP 800-161
Detailed C-SCRM practices and controls
Designing a complete programme
NIST CSF 2.0
Cybersecurity governance and risk structure
Connecting supply chain risk to enterprise cyber risk
NCSC guidance
UK-focused principles and implementation guidance
UK organisations and public sector teams
ISO 27001
Auditable supplier security controls
Management systems and assurance
NIS2 and DORA
Regulatory expectations
Relevant regulated organisations
What does an effective C-SCRM programme look like?
C-SCRM is just a bunch of supplier assessments, right? This is one of the common misconceptions we hear a lot. While assessments are a key plank of C-SCRM, an effective C-SCRM programme goes well beyond questionnaires, supplier scores, and external security scans. It should be a connected set of decisions, evidence, owners and workflows led by the security leader.
Here are the key steps to building an effective programme:
Establish governance and risk appetite: C-SCRM must be a top-down push from senior leadership. It has to be embedded into risk governance structures and aligned with your organisation’s risk appetite, not a nice-to-have bolt-on.
Build and maintain the supplier inventory: You can't manage what you don't know, so get a handle on your suppliers, what they do and what data access they have. Your inventory should include information beyond names and contract details, such as the critical business services supported and known subcontractors.
Identify critical suppliers and services: What are the key services you provide? Which suppliers enable you to carry out those services? What keeps the C-suite up at night if it goes wrong? These are the suppliers and services that are most critical.
Tier suppliers according to risk: Assess your suppliers according to their level of risk and the impact they have on your business operations. Ten tier them as low, medium, high or critical risk.
Set proportionate security requirements: Set security requirements for each supplier tier. For example, you’ll want to see stringent security controls at critical suppliers, while security certificates may suffice for lower tier suppliers.
Collect and evaluate evidence: From questionnaires and external scans to in-depth interviews and continuous monitoring tests, you need to collect evidence on these security requirements and then evaluate them according to relevance and scope.
Record findings and residual risk: Note down the inherent risk that you found about each supplier, such as the services supported and data accessed. Then note the residual risk that remains once you’ve assessed the supplier’s internal controls.
Assign and track remediation: For risks that require attention, designate an internal owner that will coordinate with the supplier throughout the remediation process, ensuring any hurdles are cleared.
Monitor suppliers and reassess when conditions change: Your suppliers are continuously changing their environment and systems, be it adding new subcontractors or redesigning services. Track these developments and take reassessments when specific event triggers occur.
Prepare for and respond to supply chain incidents. Before an incident, make sure to identify critical suppliers and services, define notification requirements in contracts and agree escalation paths. When an incident occurs, follow the existing incident-response plan, ensuring you prioritise the most critical risks first.
Measure performance and report to leadership: Track key coverage, risk, monitoring, efficiency and resilience metrics, and summarise the core risk info, so that senior leadership can make informed risk decisions.
Improve the programme over time: This is not a build it once and leave it programme. Supply chain risks are constantly changing, so you need to be continuously improving your C-SCRM programme to suit new developments.
How do you identify and tier critical suppliers?
You don’t have unlimited time and resources, so focus your attention on the suppliers that would hugely disrupt your operations if they went down or were compromised.
Start with your supplier inventory
Most organisations have a database of all their third-party suppliers. As you have contracts with these suppliers, it’s usually a spreadsheet built and maintained by Procurement. But Procurement gathers procurement information like spend and contract dates. They don’t focus on security or resilience criteria, let alone criticality. So, as a security leader, start with Procurement’s list, but then adapt it by adding:
Supplier name
Service provided
Business owner
Contract owner
Data accessed
Systems accessed
Hosting or processing location
Critical business services supported
Known subcontractors
Contract dates
Incident contacts
Current assessment status
Define supplier criticality
Supplier criticality is inherently subjective. But, at an organisational level, criticality tends to equate with impact, be it operational, financial or legal. For instance, most private sector organisations care most about revenue impact, while the public sector has a greater safeguarding responsibility.
To define criticality, you should consider:
Impact of supplier unavailability: Could your business keep functioning if the supplier goes offline?
Sensitivity of data handled: Does this supplier have access to key customer, product or financial data?
Level of system or network access: If a cyberattacker steals the supplier’s credentials what level of access to your systems or network will they get?
Privileged access: If a supplier’s credentials are compromised will they get privileged access to your systems or customer data?
Importance of the supported service: What operations would be affected: your most important business services like financial transactions or nice-to-have functions that could be done manually like recording sales calls?
Recovery-time requirements: How quickly would it take for the affected supplier to get up and running again: hours, days or weeks?
Ease of replacement: How easy is it to use external suppliers or internal mechanisms as a back-up or failover if the supplier goes down?
Regulatory or safety consequences: Will you fall foul of operational resilience, data privacy or financial regulations if this supplier is compromised?
Reliance on common fourth parties: How many of your critical service relationships are tied to the functioning of this supplier?
Separate inherent risk from residual risk
There are two types of risk to differentiate: inherent risk and residual risk. Inherent risk comes from what the supplier does and what access it has to your data and systems. Residual risk is what’s left once you’ve assessed its supplier controls. For example, if your SaaS provider holds customers’ personal data, the inherent risk is that large volumes of sensitive data sit outside your control, so a breach could mean regulatory exposure and loss of trust. But if the SaaS provider has encryption, a recent ISO 27001 certificate and contractual breach notification terms, the residual risk is noticeably lower.
Build a table of tiered suppliers
After taking those steps, you can then create a table that tiers your suppliers by criticality. But remember: this changes frequently.
Supplier tiers and assessment depth
Tier
Characteristics
Assessment depth
Critical
Supports critical services, sensitive data or privileged access
Full assessment, evidence validation, incident planning and frequent monitoring
High risk
Material access or dependency
Detailed assessment and regular review
Medium risk
Limited access or moderate business impact
Standard assessment and periodic evidence
Low risk
Minimal cyber exposure
Baseline checks, with reviews only by exception
How should organisations assess supplier cybersecurity risk?
Different risks need different assessments. While, the standard TPRM assessment practice is to send out a uniform questionnaire to new suppliers at onboarding and then reassess them on an annual basis, this fails to take into account supplier criticality or evolving risks.
In C-SCRM, you therefore need to think about the appropriate assessment depth and methods for each supplier and make sure to evaluate the evidence in the right way.
Define assessment depth
Choosing the assessment scope is more important than the frequency of the assessment as with the wrong depth, you’ll either waste effort on low-risk suppliers or wave through suppliers that actually deserve scrutiny.
The supplier’s tier is the primary factor when choosing assessment depth. For instance:
Low risk: light-touch screening and contractual clauses
Medium risk: standard questionnaire and policies review
High risk: frequent assessment of controls and validation of submitted evidence
Critical: enhanced due diligence, continuous monitoring, and incident playbooks
But the supplier’s tier alone doesn’t cut it. You should also base the assessment depth on the service provided, the data exposure and technical access, as well as relevant regulatory requirements and existing incidents.
Choose the appropriate assessment methods
Questionnaires are most organisations's go-to assessment option. While these provide a good baseline, they can't show when things change, such as a new subcontractor being added, and they only tell you what the supplier is willing to admit. You therefore need to balance questionnaires with other assessment methods like external monitoring and certificates.
Depending on the tier of the supplier and what evidence you’re looking to source, these are the methods to consider:
Supplier security questionnaires
Policy and procedure reviews
Certifications and attestations
Penetration test summaries
Audit reports
Interviews or workshops
Contractual security requirements
External security monitoring
Threat intelligence
Previous incidents
References from internal stakeholders
Evaluate evidence quality
What do these assessments actually say? Ultimately, you want to know whether a supplier has a particular control in place and how much you can trust what they've told you.
To do that, you first need to collect the evidence (by looking at whether a supplier has answered every question and attached every certificate etc) and then review the evidence (gauging whether their evidence actually supports the risk decision you're about to make).
To ensure the evidence is fresh and unbiased, evaluate it by:
Relevance
Scope
Date
Independent validation
Ownership
Applicability to the service being purchased
Record the outcome
Every review should lead to a decision you can actually stand behind. This isn’t about just having a defensible position for a regulator or an auditor. It’s about taking action to improve your supply chain security and operational resilience, so make sure every assessment produces:
Findings
Risk rating
Required remediation
Owner
Deadline
Risk acceptance or exemption
Reassessment date
Evidence trail
What each type of supplier evidence can and can't show
Evidence type
What it can show
Limitation
Questionnaire
Internal policies and control claims
Self-reported and potentially stale
Certification
Independent validation against a defined standard
Limited to its formal scope
External monitoring
Observable technical conditions
Can't see internal controls
Audit report
Detailed independent findings
May be restricted or dated
Supplier interview
Context and clarification
Requires skilled review
Are questionnaires or continuous monitoring better for supplier risk management?
This is a question we get asked a lot, but it’s a false choice. You can’t have either/or. You need questionnaires and continuous monitoring as neither approach is sufficient alone.
Questionnaires: This supplier-provided information is great for establishing a baseline, but limited beyond that. Vendor questionnaires can ascertain whether direct contractors have certain security controls in place and meet compliance regulations. However, questionnaires are not usually standardised, making it hard to compare data, and are also taken periodically, so the information is not always in date. In addition, repeated questionnaires create supplier fatigue and reduce engagement.
Continuous monitoring: You cannot proactively mitigate supply chain risks without maintaining awareness of relevant risk changes and ensuring those risk signals lead to a clear investigation, decision or action. Continuous monitoring makes this possible by tracking multiple data sources - i.e. external technical signals, independently validated evidence and internal security controls - and surfacing the material changes or updates that require your attention. But continuous monitoring does not work without the baseline controls that questionnaires provide.
It’s been heartening to see organisations move away from annual spreadsheet-based questionnaires in recent years. But 53.6% still rely on quarterly or event-triggered updates and just 40.6% of organisations constantly monitor their critical suppliers' internal security controls. The key to a robust assessment is getting a balance of questionnaires and continuous monitoring that also include certifications and direct supplier engagement.
What each assessment method is useful for
QuestionnairesUseful for
Governance
Internal policies
Access management
Incident-response processes
Business continuity
Staff security
Subcontractor management
Controls that can't be observed externally
External monitoringUseful for
Changes in observable attack surface
DNS and email security
Public-facing services
Exposed ports
Some known vulnerabilities
New technical findings
CertificationsUseful for
Independent validation
Baseline assurance
Reducing duplicated evidence requests
Direct engagementUseful for
Clarifying findings
Agreeing remediation
Understanding service-specific context
Coordinating incident response
How often should supplier cybersecurity risk be reassessed?
An ISO 27001 certification is valid for three years. Most security questionnaires are checked on a yearly basis. But supply chain cyber risk doesn't sit still. These static assessments reveal a snapshot of a supplier’s controls at one point in time, but they fail to keep track of your supplier’s changing environment or your evolving supply chain cyber risk.
That’s why the when, who and how of reassessments should align with your supplier criticality and meaningful changes in the supplier relationship, not an arbitrarily marked date in the calendar. For instance, a high-risk supplier might need a reassessment sooner than expected if it’s acquired by another company while a low-risk supplier with a stable relationship likely doesn’t need a review as often as yearly.
As a general rule, reassess suppliers according to their risk level:
Critical suppliers: continuous monitoring plus formal review at least annually
High-risk suppliers: annual or risk-triggered review
Medium-risk suppliers: every one to two years
Low-risk suppliers: lightweight checks or reviews in exceptional circumstances
Reassessment event triggers
While you can outline the cadence and detail of a reassessment according to a supplier’s risk level, there are also specific events that can trigger reassessments for even the least risky suppliers.
Consider a reassessment if the following happens:
Material service changes. If the supplier changes what service it provides for you.
New data access. If you give an existing supplier more privileged access to your systems or data.
New system integrations. If a supplier changes its own systems in a meaningful way, such as adding an AI overlay.
Major control changes. If, for example, there are changes to its security policies or data encryption procedures.
Security incidents. If the supplier suffers a breach.
Mergers or acquisitions. If the supplier acquires or gets bought by another company.
Expired certifications. If their standards or certificates expire.
Significant external findings. If your external monitoring finds out about a vulnerability that they have not disclosed to you.
New subcontractors. If the supplier takes on a newsubcontractor, which could lead to greater fourth-party or concentration risk.
Changes in supplier criticality. If a supplier suddenly becomes more critical to you (i.e. your backup folds and it’s now the only provider for a critical service), it needs to be reassessed according to this new risk level.
Regulatory changes. If new regulations become law, such as the upcoming UK Cyber Risk Bill, or new rules are announced, such as DORA’s critical suppliers regime.
Repeated missed remediation deadlines. If there are repeated instances of delayed or ignored requests for remediation.
How should supplier risks and remediation actions be managed?
Completed questionnaires are not the point of a C-SCRM programme. Every time you identify and assess a supply risk, it should lead to a tangible action, be it simply documenting the decision or triggering a review. This is particularly important when a clear risk is surfaced and warrants remedial action.
Here’s how you can make sure that clear risks are noted, prioritised and remediated.
Convert assessment findings into clear risks. The evaluation should be able to identify clear risk from the assessment findings, such as highlighting a concentration risk if they share the same critical provider. The reviewer should then be able to make a judgement call on the follow-up action, be it recording the outcome or requiring remediation.
Define risk severity and business impact. Every risk should be considered holistically according to its ultimate impact on the business. All the context - from the services they provide, the critical business function they support and the impact of regulatory non-compliance - must be taken into account when defining risk severity.
Assign internal and supplier owners. Not every risk is going to require the CEO from your company calling the CEO of the supplier, so delegate responsibility for mitigating this risk to someone from in your security team that will lead the remediation action with the supplier. You also need to designate a POC at your supplier for seamless engagement.
Agree remediation actions. Remediation depends on the risk: perhaps it’s adding a control, setting up MFA or finding a new subcontractor (so you don’t have a concentration risk). Each action must be agreed with the supplier.
Set realistic deadlines. Keep in mind that the suppliers also have different timelines and priorities too. If they're dealing with an emerging threat, remediation of your risk may be a lesser priority. If they’re being onboarded, they have a financial incentive to get back to you sooner rather than later. Be cognisant when setting deadlines.
Collect evidence that remediation is complete. Trust and verify. At a base level, you need to believe that suppliers are telling the truth when they complete assessments or remediation. But for some critical elements, ask for verification and evaluate this evidence.
Record risk acceptance and expiration dates. Even if the risk is deemed manageable, that categorisation doesn’t last forever. As the threat landscape changes, ‘manageable risk’ might become more critical risk, so it’s worth setting an expiration date for your risk acceptance and then reviewing again.
Escalate overdue high-risk actions. Don’t act on a one-in, one-out rule of risk mitigation. Evaluate risks as they emerge and then prioritise the most important risks. Escalate any high risk to the top of your to list, especially if it's overdue.
Connect supplier findings to the central risk register. You should have a central risk register that highlights all current risks, their status, their expiration dates and the owners. Make sure to update this.
Reassess residual risk after remediation. Risks are continuous and evolving. A supplier might become lower risk by adding controls during remediation, but you still need to reassess this new residual risk and take the appropriate action.
Remediation workflow
From finding to decision
Finding identifiedAn assessment or monitoring alert surfaces a risk, issue or control gap.
Assess impactJudge severity, likelihood and exposure against the services the supplier supports.
Remediate or mitigateAgree actions with the supplier to bring the risk to an acceptable level.
ValidateCollect evidence that the fix is in place and working.
DecideChoose one of three outcomes and record it with an owner and review date.
Three possible outcomes
AcceptThe residual risk sits within tolerance. Set an expiry date for the acceptance.
EscalateThe risk needs senior review or action the security team can't take alone.
ExitReplace the supplier or end the relationship.
How do you manage fourth-party and concentration risk?
One of the biggest blind spots in C-SCRM are the cyber risks emerging beyond direct third parties. Our 2026 survey found that only 30% of security leaders can see their full subcontractor network beyond direct vendors. But this wide network of fourth and nth-party connections is a minefield of potential cyber risks. Even if you’re unaware of fourth-party connections or deeper tier concentration risks, an outage or breach can leave you dealing with the financial, operational, reputational and regulatory consequences.
Here’s why you should take them seriously and how to address them.
Managing fourth-party risk
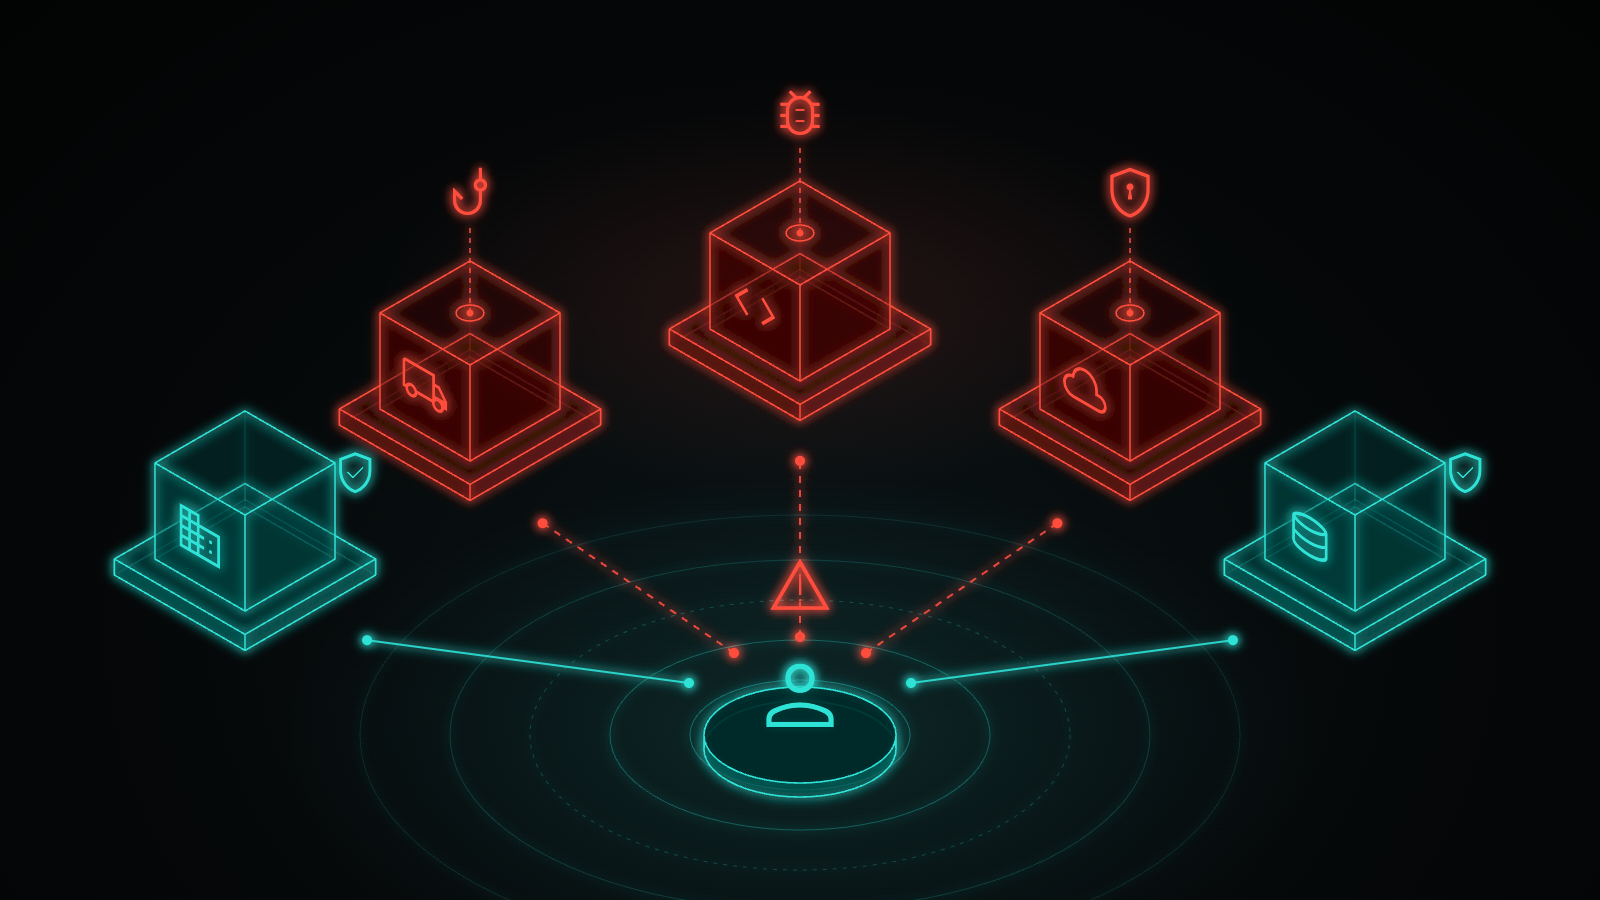
Fourth parties are your suppliers' suppliers.If there’s an outage or breach at one of your fourth-party connections, then all connected third-party suppliers could be affected, effectively removing their services simultaneously and directly impacting your operations.
As you don’t have a contractual agreement with fourth-party vendors, you’re often unaware of their existence and you cannot carry out contractly-obliged supplier assurance on them. But that doesn't mean you should just ignore fourth-party risk as it can lead to:
Critical service disruption: A critical third-party supplier may be unable to deliver its service when an underlying fourth-party provider it relies on, fails.
Data and privacy exposure: Direct suppliers may share or store your data with fourth-party sub-processors that can become exposed.
Privileged access: Technology providers used by some direct suppliers may have highly privileged access across several customer environments.
Cascading impact: Whether it’s cyberattackers actively targeting weaker links as a way to infiltrate bigger fish upstream or simply a vulnerability at fourth party flowing through to you, fourth-party breaches are becoming a common supply chain incident.
Managing concentration risks
Concentration risks represent single points of failure within the supply chain where one incident can significantly limit your ability to carry out key business functions. There are two main types of vendor concentration risk: when you rely on a supplier too heavily to deliver a critical service (and there are not many alternatives) or when multiple suppliers are resting on the same underlying connection, usually a tech provider.
While our research found the most common concentration risks come from the giant hyperscalers Google, AWS, Microsoft, Salesforce and HubSpot, vendor concentration risk can occur with almost any type of supplier, even low-spend SaaS tools that don’t require procurement screening. Here are the main forms and impacts of vendor concentration risk:
Direct supplier concentration. When one vendor supports multiple critical business functions. If that vendor goes down, so do those functions.
Technology and cloud concentration. When multiple services or suppliers depend on the same cloud platform or software provider. If there’s an incident, it can stop you from operating in your usual way.
Geographic and jurisdictional concentration. When critical operations all sit within the same region where a change of policy or national emergency could take them offline.
Service and operational concentration. When separate vendor relationships depend on one shared fourth-party, such as a payment provider. If they go down, so do multiple services simultaneously.
How to address fourth-party and concentration risk in C-SCRM
Completely eradicating fourth-party or concentration risk isn’t realistic. But having known, justified and survivable concentration risk is where you want to be. Standard C-SCRM supplier assessments record each direct supplier's own controls, but rarely show fourth-party connections, let alone the security posture of these fourth-party suppliers. So to protect your organisation (and save your team’s time), focus on the fourth-party and concentration risks that affect your most critical services.
Identify your critical services: Look at your supplier list and find the services whose disruption would create the greatest operational, financial, regulatory or customer impact.
Collect key dependency information: Ask critical suppliers that support these services about their critical sub-contractors, sub-processors, infrastructure providers and technologies. This will help you connect each critical service with its nth-party dependencies.
Validate and structure the information: Corroborate the vendor’s intel by asking for contracts, their supplier questionnaires, technical architecture and software composition information. Reach out to the fourth parties for confirmation.
Map important fourth-party dependencies: Don't start from scratch. Map the fourth-party suppliers of the suppliers that you’ve already flagged as critical or high-risk.
Identify shared dependencies: Look for providers used by several critical suppliers. These could be obscure, low-spend SaaS tools or giant hyperscalers.
Assess potential blast radius: Consider what would happen if a fourth party connection went offline or suffered a breach. Look at your map and see how it would cascade through the system.
Develop coordinated response plans: Use this dependency knowledge to inform your failover plans and Disaster Recovery strategy, including how they would notify you if something goes wrong and the remediation protocol. For each critical dependency, define the expected notification route, required evidence, escalation threshold and the alternative service or workaround.
Fourth-party and concentration risk
How one shared provider can reach several business services
Your organisation
OrganisationContracts with three direct suppliers
Direct suppliers (third parties)
Supplier 1Provides softwareRelies on shared cloudUses subcontractor
Supplier 2Provides supportRelies on shared cloud
Supplier 3Provides security servicesRelies on shared cloud
Their suppliers (fourth parties)
Shared cloud providerUsed by all three direct suppliersConcentration point
SubcontractorUsed by Supplier 1 only
Affected business services
Customer portalAt risk if the cloud provider or Supplier 1's software goes down
Payment processingAt risk if the cloud provider or Supplier 2's support goes down
Data and reportingAt risk if the cloud provider or Supplier 3's security services go down
Email and communicationAt risk if the subcontractor or Supplier 2's support goes down
A cloud outage here takes out three suppliers at once, and through them three business services, even though you have no contract with the cloud provider. Your supplier inventory alone won't show you that.
How should organisations respond to a cybersecurity supply chain incident?
Don’t simply add the incident to your to-do list as it may require immediate prioritisation.
Just as you assess suppliers by criticality, you should also respond to incidents by prioritising the incidents that could affect your most critical suppliers.
Use this seven-step incident workflow:
Confirm the event: Verify the incident by looking at trustworthy sources, such as the NCSC or NSA, and check if the vulnerability has been given a CVE score by NIST (a score above 9.8 is attention-worthy).
Identify supplier exposure: Check whether the incident affects your direct suppliers and whether the affected suppliers are critical. Then review the fourth-party connections of your critical suppliers to determine if they have a link with an affected organisation and what your potential exposure is.
Map affected services: Consider which of the affected suppliers are critical to your business functions. Estimate the blast radius to see how you're affected (i.e. which route would it take for a breach to reach you).
Collect evidence: Contact the most critical suppliers and collect evidence from them. In particular, ask them:
How do you use the affected product, component or service?
Which customer data, systems or services could be affected?
What containment and remediation actions have already been completed?
Contain and mitigate: Revert to your incident playbook and take actions based on impact criteria. This could be switching to an alternative supplier or spinning up backup systems.
Communicate and escalate: Communicate directly with the affected suppliers and get regular updates. Use your real-time data and network visualisations to escalate incidents to C-suite level if needs be (i.e. you need your CEO to call their CEO to make it a priority).
Validate recovery and update risk: Establish timelines for affected suppliers to respond and ask for proof they’ve remediated the issue. Even if it's a minor threat, make sure to validate recovery and take heed from lessons.
Checklist
Supply chain incident response checklist
1Before an incident
2During an incidentQuestions to answer quickly
3After an incident
Which C-SCRM metrics should security leaders report?
You’re in charge of the C-SCRM programme. You need to report the progress to the CEO and/or board. Explaining your C-SCRM programme in detail is not enough. You need to speak their language: metrics.
When updating the board, make sure to deliver evidence on improved supplier coverage, faster decisions, reduced exposure, stronger incident readiness and the more effective use of team capacity. Use these metrics.
Board reporting
C-SCRM metrics to report to leadership
Coverage metricsShows: supplier coverage
% of suppliers inventoried
% of critical suppliers identified
% of critical suppliers assessed
% with current evidence
% with named business owners
Risk metricsShows: reduced exposure
Unresolved critical and high risks
Residual risk by supplier tier
Overdue remediation actions
Risk acceptance volume and age
Suppliers with repeated control failures
Monitoring metricsShows: faster decisions
Material supplier changes detected
Incidents affecting suppliers
Time to identify affected suppliers
Time to contact suppliers
Time to assess business impact
Efficiency metricsShows: use of team capacity
Average assessment time
Supplier response time
Repeated evidence requests avoided
Analyst hours spent on administration
Procurement delays caused by assurance
Resilience metricsShows: incident readiness
Critical services with mapped supplier dependencies
Critical suppliers with tested incident contacts
Concentration risks identified
Suppliers with recovery plans reviewed
But remember: these metrics help shape the story, they are not the story. Ultimately, the board doesn’t really care how many suppliers you have in your inventory or how many assessments you’ve completed. They want to know what supply chain risks are present, what the impact could be (i.e. revenue drop, reputational damage, regulatory non-compliance), and what you’re doing about it. These metrics help you give them a defensible story to take to the media, shareholders, customers and regulators.
How can organisations scale C-SCRM without creating excessive operational burden?
There is a simple way to build an effective C-SCRM programme even if you have minimal budget or resources: prioritisation.
Don’t attempt to monitor every supplier, threat and dependency at the same depth. Prioritise the most critical suppliers and focus on the supply chain cyber risks that will have the greatest disruptive impact on your business. Here’s what you should do.
Prioritise rather than assess everything equally. Apply deeper assurance to critical relationships, use baseline requirements for lower-risk suppliers, and escalate in exceptional circumstances.
Standardise the process. Use consistent control frameworks, standardise evidence requirements, define clear review workflows and use common risk language.
Reuse existing evidence. Avoid asking suppliers for the same information repeatedly and collaborate with peers in the supply chain regarding supplier due diligence they’ve already done.
Automate administration. While automation should not replace human risk decisions, automate the likes of supplier invitations, evidence reminders, certificate expiry alerts, review scheduling, and remediation tracking.
Improve supplier engagement. Set up a direct comms channel with your POC at each supplier where you canrequest evidence, give suppliers a clear route to respond, and share findings and remediation expectations.
Use event-driven workflows. Focus your security analysts on: material changes, high-risk findings, overdue remediation, affected critical services and incidents requiring action.
How Risk Ledger supports cybersecurity supply chain risk management
Running a C-SCRM programme at scale requires fresh supplier evidence, streamlined assessment workflows, and frictionless supplier collaboration that help you focus on the most critical suppliers and risks. That’s what Risk Ledger delivers.
Our platform brings together a standardised TPRM engine, live network mapping of supplier relationships, proactive emerging threat management and a dedicated supplier comms channel, so you can easily identify risks, evaluate their criticality and prioritise action.
With Risk Ledger, you can:
Reduce duplicated supplier assurance. All suppliers answer a common security assessment based on key regulations and standards, which are personalised to your own unique organisational circumstances, creating a common language of risk for the entire ecosystem. Suppliers then maintain a single, standardised security profile, which they can update and share with all existing and prospective customers, cutting out duplicated assessment time for both you and them.
Keep supplier risk information current. Our platform provides continuous monitoring of updates to suppliers' security controls, including when suppliers add new subprocessors or redesign services, so you can review these changes and react quickly.
Prioritise the risks that require action. Instead of sorting supplier risk by spend or chronology, we help you identify and tier suppliers based on their actual impact to your business operations. With our real-time risk signals, intuitive dashboards and simulated disruptions, you can instantly assess the potential impact of emerging risks and take the appropriate action.
Understand wider dependencies. Get a network view of supplier relationships beyond your third parties. Our network map shows all your third, fourth and nth-party relationships on one map, so you can see hidden fourth party risks, identify concentration risks and better understand how a supply chain risk could cascade through the ecosystem. You can make risk-based decisions and take premeditated action to mitigate disruptions.
Improve incident coordination. Our platform provides a direct channel to communicate with POCs at each supplier whether it’s regarding a specific control or during an incident. The platform also enables you to launch and track remediation workflows (i.e. with notifications when suppliers have remediated a risk) without the manual chasing.
Looking to kickstart or improve your C-SCRM programme? Follow this checklist:
Create a complete supplier inventory
Assign an internal owner to each material supplier
Identify critical business services
Map suppliers to the services they support
Define supplier criticality criteria
Tier suppliers according to inherent cyber risk
Set proportionate control and evidence requirements
Assess critical and high-risk suppliers
Record findings, remediation and residual risk
Establish scheduled and event-driven reassessment
Monitor relevant changes between reviews
Maintain current supplier incident contacts
Map important fourth-party dependencies
Identify concentration and single-point-of-failure risks
Integrate suppliers into incident-response planning
Report coverage, risk, remediation and resilience metrics
Review and improve the programme regularly
Cybersecurity supply chain risk management FAQs
How should organisations prioritise suppliers when they cannot assess every supplier in depth?
Match assessment depth to each supplier's risk level, weighing the service it provides, its data exposure and technical access, relevant regulatory requirements and any previous incidents. For example:
Low risk: light-touch screening and contractual clauses
Medium risk: standard questionnaire and policy review
High risk: frequent assessment of controls and validation of submitted evidence
Critical: enhanced due diligence, continuous monitoring and incident playbooks
What evidence is sufficient to make a defensible supplier cyber risk decision?
Sufficient evidence is relevant to the service you're buying, covers the right scope, is recent and, for critical suppliers, is independently validated. In practice that means balancing point-in-time assessments such as questionnaires with continuous monitoring, drawing on sources like these:
Supplier security questionnaires
Policy and procedure reviews
Certifications and attestations
Penetration test summaries
Audit reports
Interviews or workshops
Contractual security requirements
External security monitoring
Threat intelligence
Previous incidents
References from internal stakeholders
How can organisations keep supplier risk information current between formal assessments?
Use continuous monitoring to track external technical signals, independently validated evidence and changes to suppliers' internal controls. Good monitoring surfaces only the material changes that need attention, such as a supplier redesigning its service or taking on a new subcontractor, and each change should lead to a review, a decision or a triggered reassessment.
How should C-SCRM account for fourth-party and concentration risk?
Eliminating fourth-party or concentration risk isn't realistic, so aim for concentration risk that is known, justified and survivable. Start with the fourth-party dependencies behind your critical suppliers and services, look for providers several of them share, assess the potential blast radius of an incident at each one, and build those dependencies into your response and recovery plans.