Capability

Review Supplier Security

Gain a complete view of supplier security, prioritise supplier reviews based on business risk and make confident decisions with up-to-date evidence.

Trusted by
Succession Wealth
Octopus Investments
Grant Thorton
Upvest
Crowe
Succession Wealth
Octopus Investments
Grant Thorton
Upvest
Crowe

Manage supplier reviews from one place

From onboarding suppliers to maintaining continuous assurance, Risk Ledger brings every stage of the supplier review process together in one platform.

01

Onboard & prioritise

Build your supplier inventory quickly by connecting to existing suppliers or onboarding new ones, then prioritise reviews based on business risk.
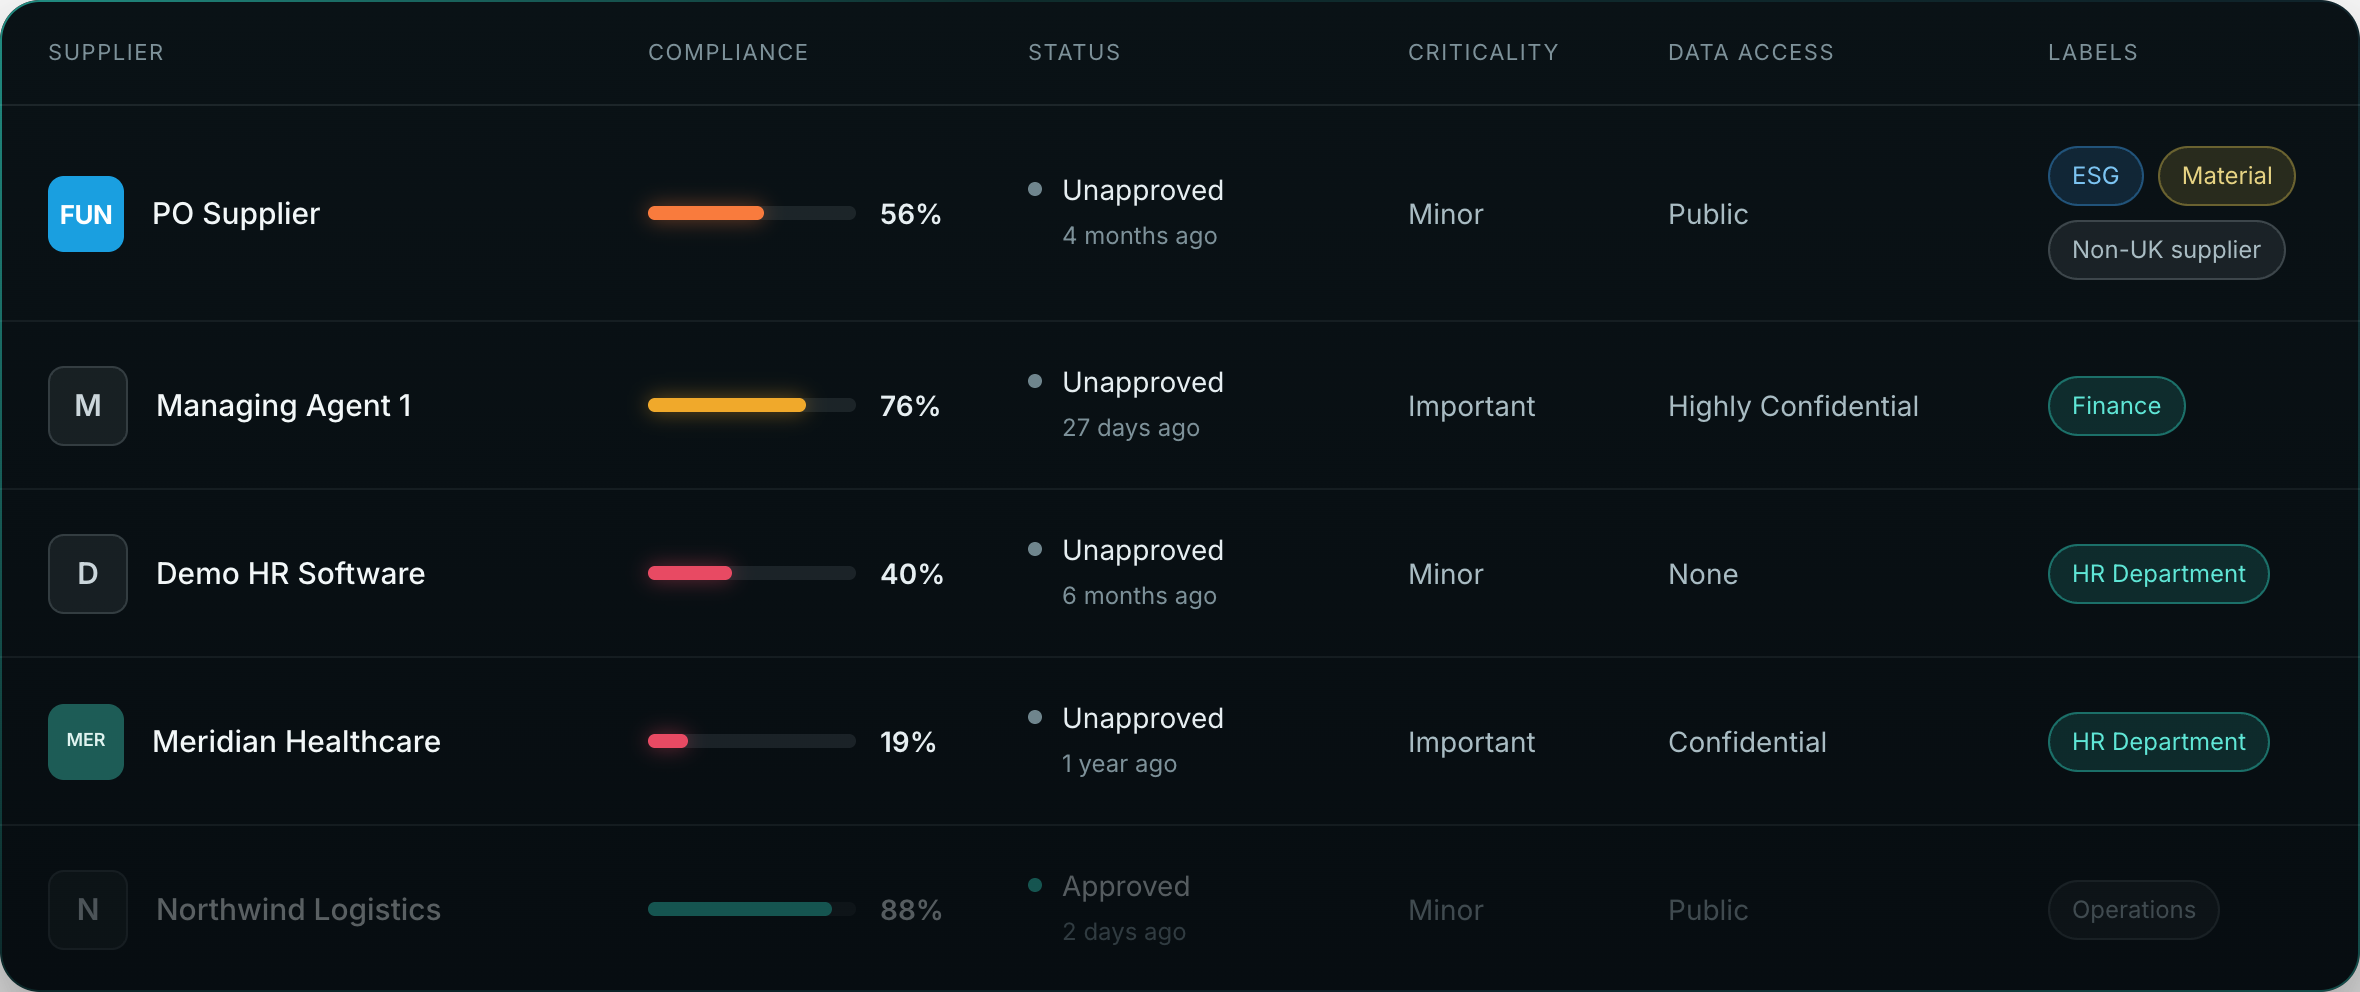
Connect to suppliers already on the Risk Ledger network or invite new suppliers to start the review process.
Invite new suppliers individually or in bulk, and send automatic chasers when needed.
Prioritise suppliers by criticality, confidentiality, PII and your unique business context.
Add custom tags and labels to better categorise and prioritise suppliers, informing how you review them later on.
02

Capture data & evidence

Centralise supplier security information in one place, from assessment responses and certifications to supporting evidence and product-level assurance.
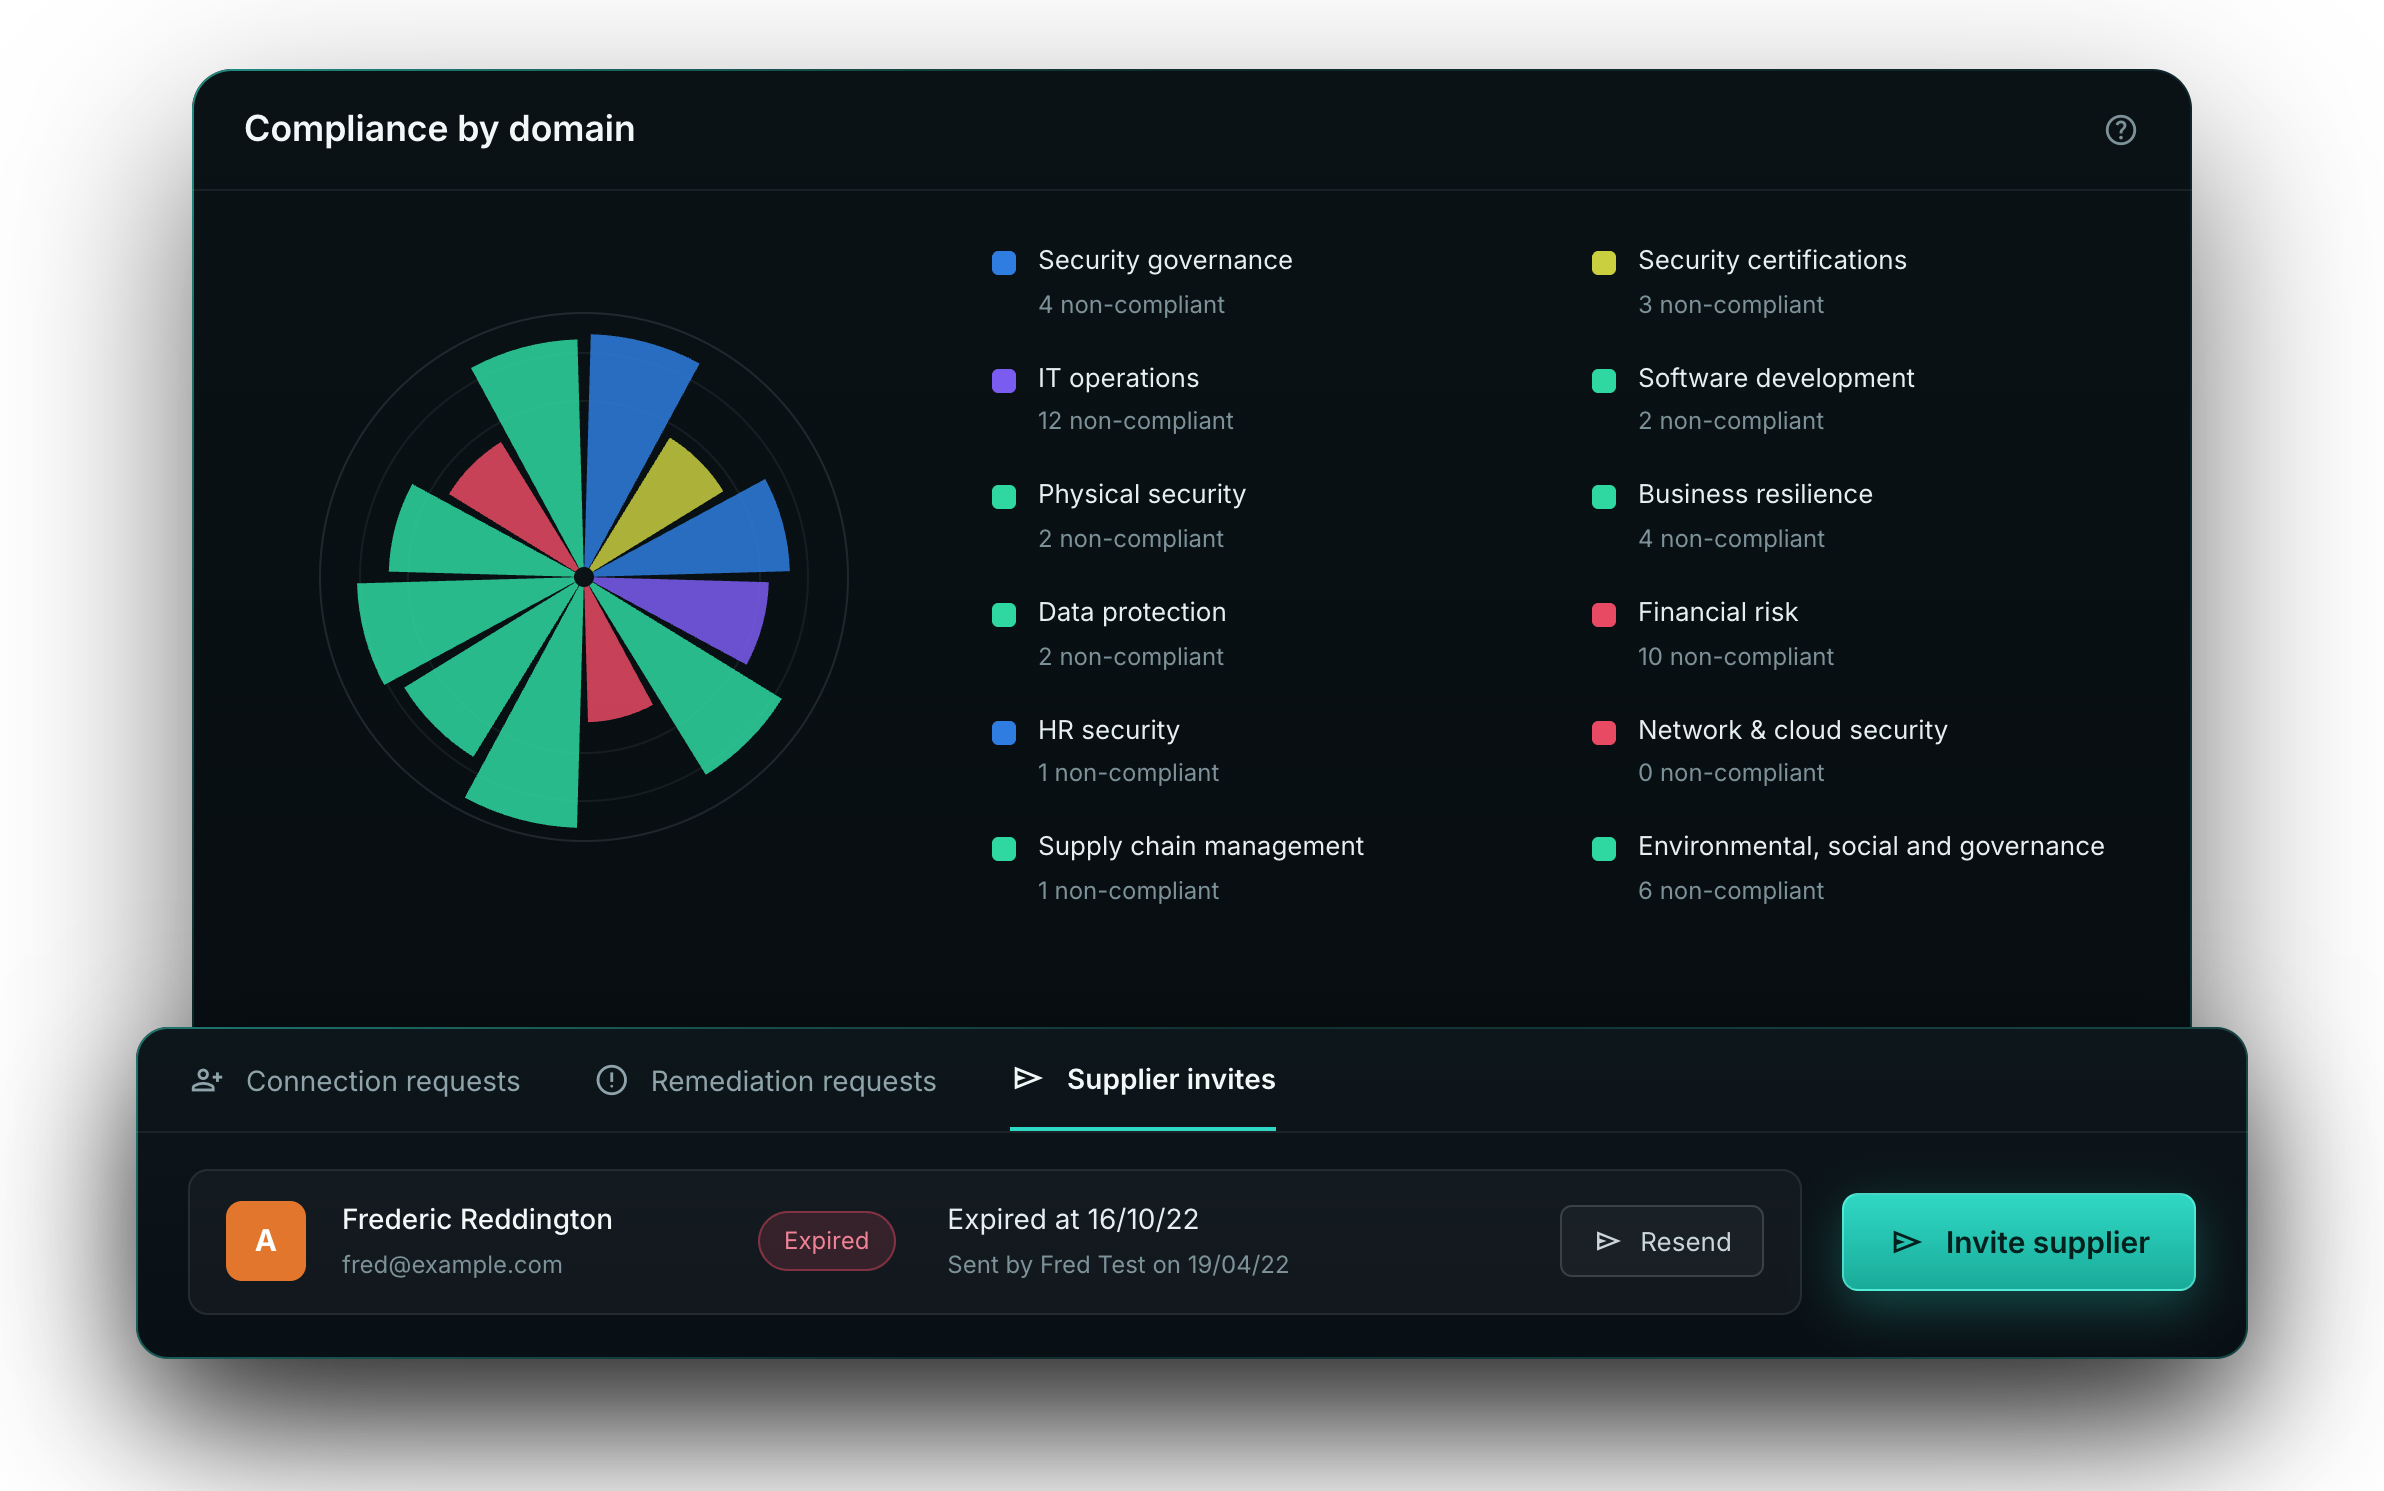
Capture core supplier security data using the Standardised Assessment Framework
Tailor assessments with the Flexible Framework and Add-ons to reflect what matters to your business
Run product-level assurance for suppliers that deliver multiple services or products
Store all evidence and certifications within each Supplier’s Profile
Check whether suppliers hold the required ISO and Cyber Essentials certifications
03

Assess & review

Review supplier data and evidence with structured workflows, with all your security work stored in one place.
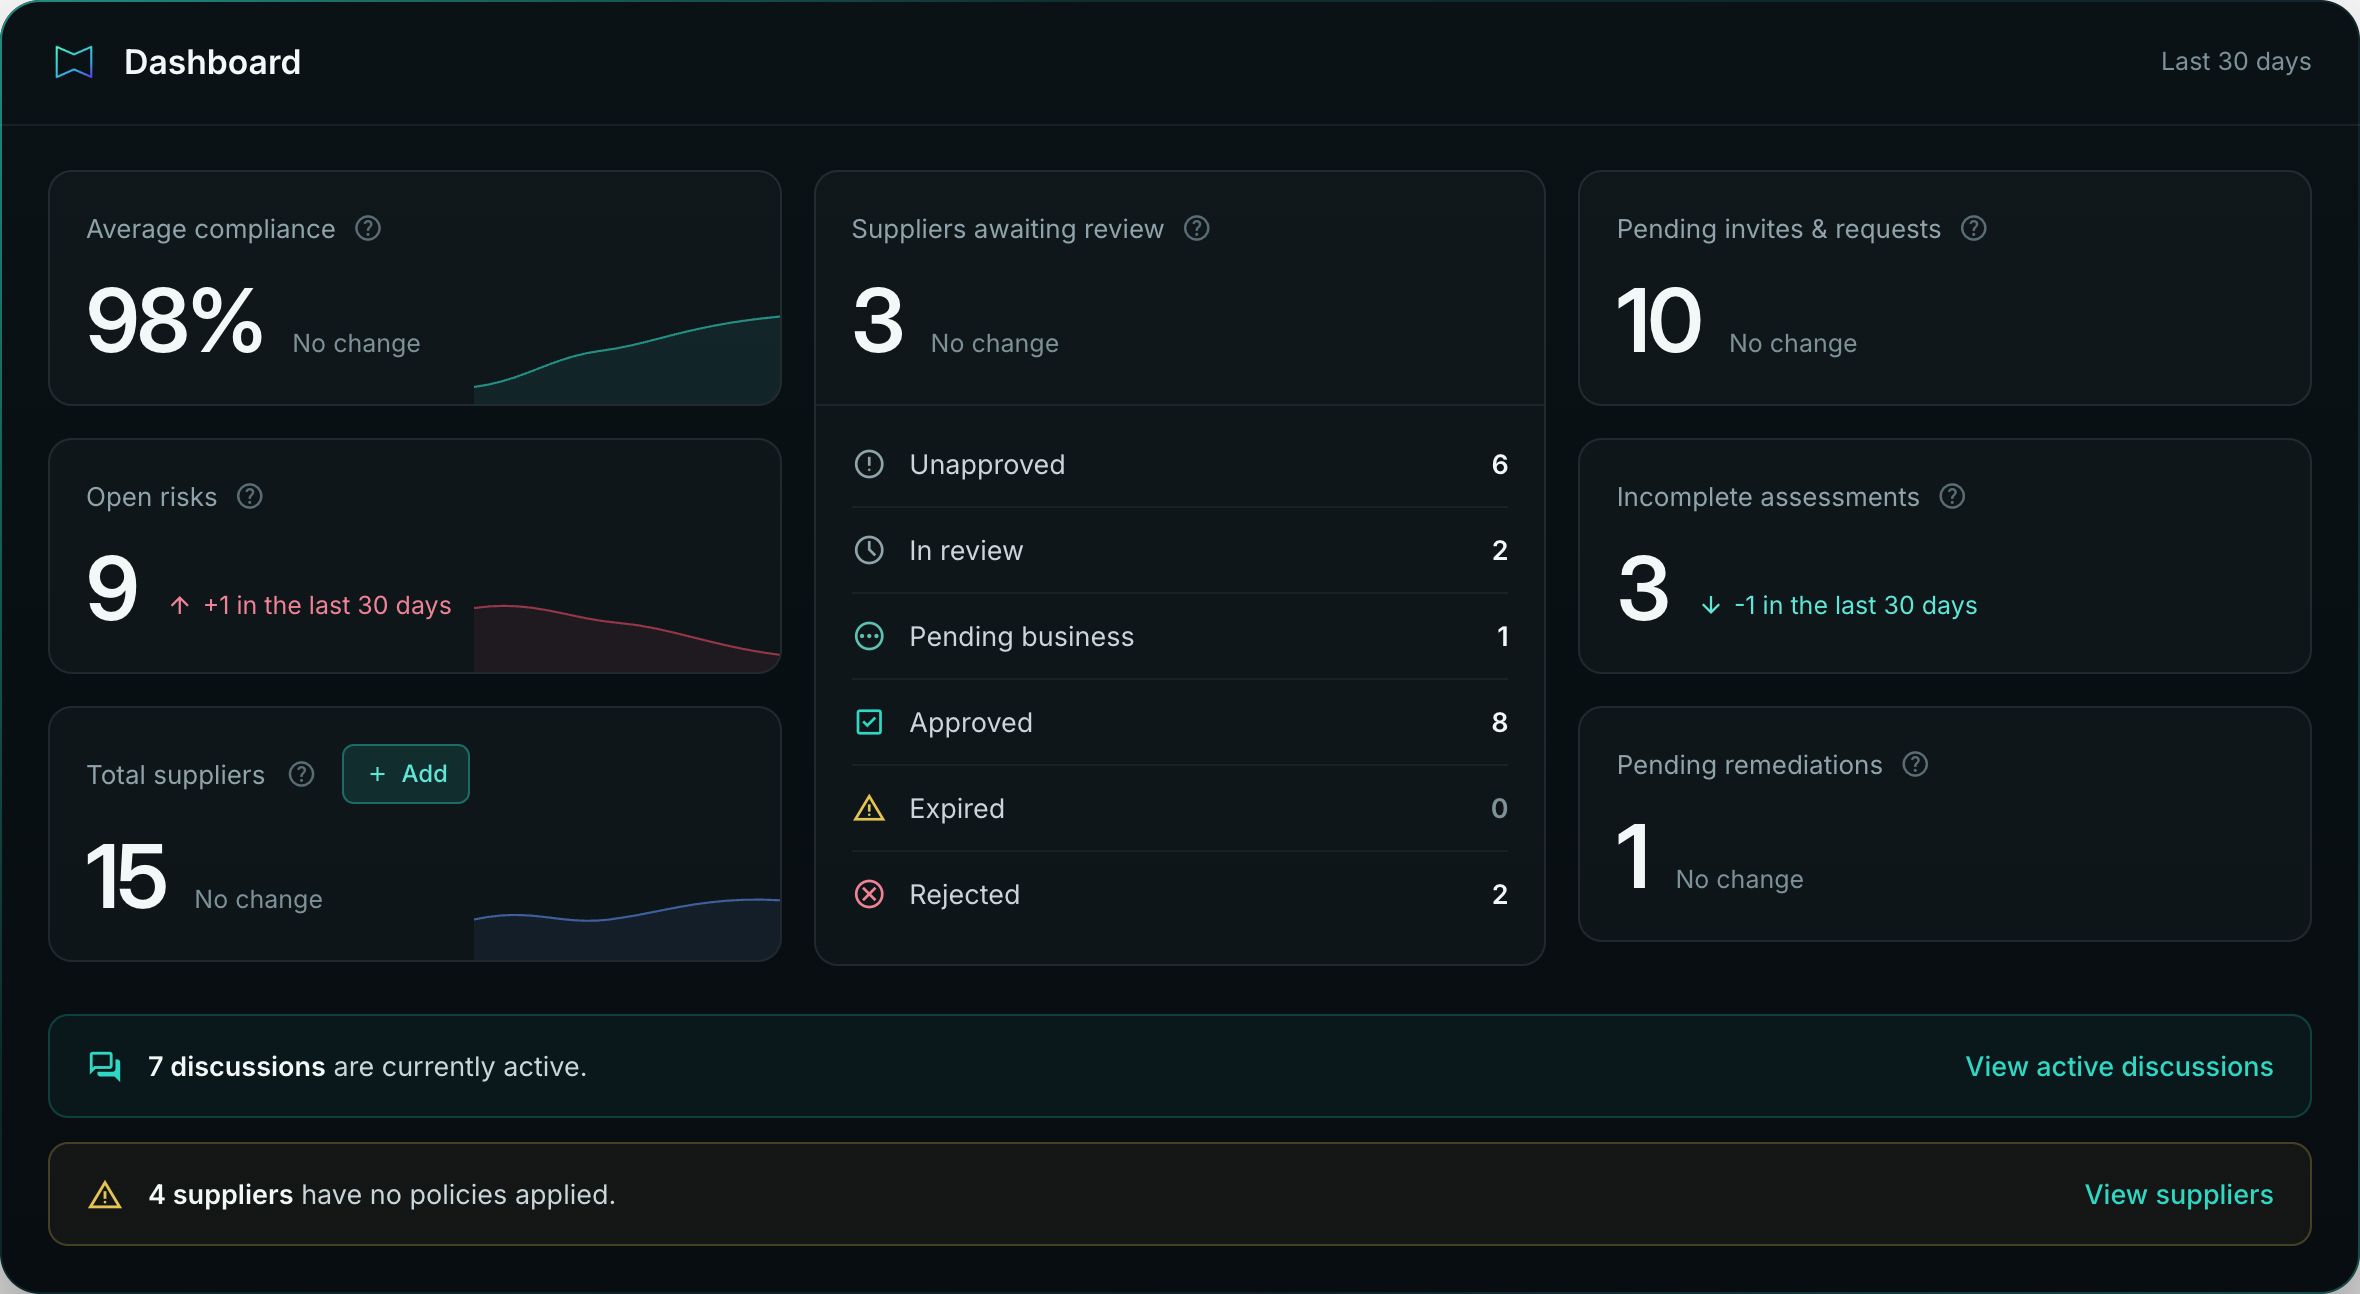
Assign reviewers, track actions and collaborate across teams
Use AI to run first-pass reviews and draft summaries
Add private notes, open risks, start a discussion with a supplier and request remediations.
Scale assessments with consistent review criteria and audit-ready records
04

Ongoing assurance

Keep supplier assurance current with continuous visibility into changing risk.
Get notified of changes when a supplier updates their profile
Schedule reassessments for suppliers to update their profile
Add External Monitoring to their assessment data for continuous monitoring of their security posture

Smarter Assessment Workflows

Turn assessment data and evidence into clear decisions and actions. AI helps teams move faster by surfacing what matters most, while keeping a human in the loop for context, judgement and final decisions.
Supplier Summary — Get a concise view of each supplier’s strengths, gaps and priority issues, so reviewers know where to focus. Share a clear, decision-ready summary with stakeholders.
Domain Review Agent — Run a first-pass review that summarises findings by domain, highlights the issues most likely to affect your organisation, and recommends next steps — from starting a discussion to raising a remediation or opening a risk. Reviewers stay in control and decide what happens next.

Create a single source of truth for supplier security

Bring supplier reviews, security data, evidence and key documents together in one place, so every team has a trusted, up-to-date view of supply chain security.

Scattered supplier reviews

Reviews spread across spreadsheets, inboxes and point-in-time assessments

Teams relying on outdated evidence from static supplier assessments

No single view of supplier security posture, actions or decisions

Connected supplier assurance

All reviews, supplier profiles, evidence and certifications held in one shared workspace

Security data that stays current as suppliers update their profiles

A complete record of assessments, discussions, remediations and decisions

Centralise supplier security data
Keep assessment responses, evidence, certifications and supporting documents together in one place.
Give every team the same view
Help security, procurement, risk and business stakeholders work from the same trusted supplier record.
Build an audit-ready record
Maintain a clear history of reviews, discussions, remediations and decisions across your supplier base.

Tailor reviews to each supplier

Set different review requirements based on supplier criticality, data access and your own business context. Custom policies let you define what each supplier needs to demonstrate, while keeping reviews consistent across your programme.

1

Set requirements that reflect risk

Apply different requirements based on supplier criticality, access to confidential or personal data, and other criteria that matter to your organisation.
2

Configure your own policies

Use pre-built policies or create custom policies and labels that reflect how your organisation categorises and reviews suppliers.
3

Review suppliers against your requirements

See supplier compliance against the policies that apply to your specific relationship, so reviewers can focus on the controls that matter.
4

Understand supplier alignment with industry frameworks

Use suppliers’ existing Risk Ledger assessments to assess alignment with CAF, Cyber Essentials, ISO 27001, NIST CSF and Cloud Security Principles, without the manual mapping.

Everything you need to review suppliers at scale

Bring every stage of your supplier review process together in one platform - from onboarding and assessments to collaboration, reporting and audit readiness.
Supplier onboarding
Connect to suppliers already on the Risk Ledger network or invite new suppliers in bulk to accelerate onboarding and start assessments sooner.
Standardised assessments
Run consistent supplier assessments using the Standardised Assessment Framework across your supplier base.
Structured reviews
Review supplier responses and supporting evidence together using structured workflows that help teams make informed decisions faster.
Custom policies
Tailor assurance requirements using supplier categorisation and custom policies that reflect each supplier relationship.
Reporting & oversight
Track supplier activity, monitor remediation progress, and demonstrate due diligence with reporting built for stakeholders and auditors.
Complete audit trail
Maintain a complete record of supplier assessments, discussions, decisions and approvals so you're always ready for governance and audit.

Built on a connected network

Risk Ledger connects organisations and suppliers through a shared network. Connect to suppliers already on the Risk Ledger network or onboard new suppliers, giving your team faster access to updated security information while reducing the effort needed to get reviews underway.

Accelerate supplier onboarding

Connect to existing suppliers or invite new suppliers to start reviews sooner.

Reduce duplicate effort

Access security information suppliers already maintain instead of collecting it from scratch.

Maintain continuous assurance

Benefit from ongoing supplier updates that help keep your view of risk current.

Trusted by organisations protecting complex supply chains

From financial services to public sector, organisations use Risk Ledger to standardise supplier assurance, reduce manual effort and improve supplier oversight across their supply chains.

CUSTOMER STORY
"The standardisation of processes have reduced administrative overhead and enabled our team to focus more on risk analysis rather than data collection."
Paul Daniels
VP, Global Technology & Cybersecurity, Pentland Brands
TRUSTED BY SECURITY TEAMS
4.4/5 on
Based on 120+ verified customer reviews
"Risk Ledger has become an essential tool in our third-party due diligence process. It simplifies supplier onboarding and risk assessment by providing a centralised platform where vendors can maintain and share their security profiles.”
View security documentation
Succession Wealth
Octopus Investments
Grant Thorton
Upvest
Crowe
Succession Wealth
Octopus Investments
Grant Thorton
Upvest
Crowe
FAQ

Common questions about supplier assurance

How do we prioritise which suppliers to assess?

Risk Ledger helps organisations prioritise supplier assessments based on supplier criticality, business context and current risk, so reviews are focused where they have the greatest impact.

Can different teams collaborate on supplier reviews?

Yes. Security, procurement and business stakeholders can review suppliers, manage actions and track assurance activities together within a shared workflow.

How does Risk Ledger support regulatory compliance?

Risk Ledger helps organisations demonstrate due diligence through consistent supplier assurance processes, structured evidence collection, reporting and a complete audit trail.

How does supplier onboarding work in Risk Ledger?

Risk Ledger supports onboarding for both your organisation and your suppliers. Connect to suppliers already on the Risk Ledger network or invite new suppliers individually or in bulk. Suppliers can maintain a reusable security profile that is shared securely with connected customers, helping organisations start reviews sooner while reducing duplicated effort.

Do suppliers have to pay for a Risk Ledger profile?

No. We believe that supplier engagement is key to building Active Supply Chain Security, which means we want to remove as many barriers to entry for suppliers as possible. Suppliers can sign up for free on Risk Ledger, get access to our extensive Knowledge Base, and get free scan data to improve their security posture.

Make supplier reviews work at scale

Standardise supplier assessments, focus review effort where risk is greatest and keep supplier information current as your programme grows.